From Jamf Console to Code, Part 1: Why IaC Matters
Policies, profiles, and Smart Groups are familiar territory for Jamf admins. Infrastructure as code adds a reviewable, repeatable way to manage selected parts of that environment, without requiring an all-at-once migration.
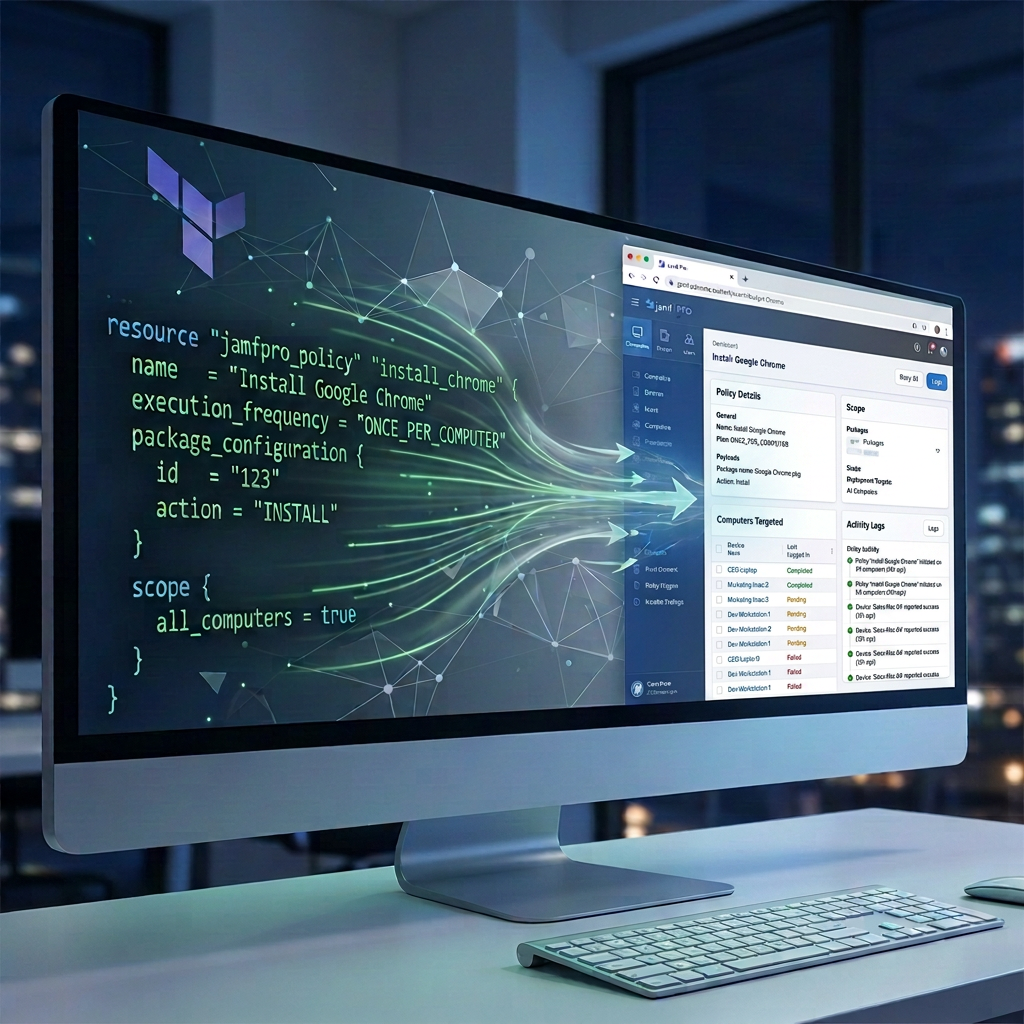
The goal is not to stop using the Jamf Pro interface. It is to make important changes easier to review, repeat, and trust.
If you manage Jamf Pro, you probably know the rhythm: open a policy, adjust its scope, save the change, and move on to the next task. That workflow is direct and useful. It is also easy to lose track of exactly what changed, why it changed, and whether the same configuration exists in another environment.
Infrastructure as code (IaC) offers another way to manage Jamf Pro: describe selected configuration in files, keep those files in version control, and review a proposed change before it reaches your tenant.
This is not about replacing the Jamf Pro interface or moving every object into Terraform. It is about building a dependable change process for the parts of Jamf you choose to manage as code.
The console is great for making a change. What happens after?
Imagine that you need to update the scope of an application installation policy. In the Jamf Pro interface, you can make that change quickly. But later, someone may ask:
- Which Smart Group was added or removed?
- Who approved the change?
- Was production changed the same way as development?
- Did the change affect anything else?
- How would we recreate this configuration in a replacement tenant?
The Jamf Pro interface is not the problem. The challenge is that a sequence of console edits does not automatically give your team a consistent, reviewable record of desired configuration.
A ticket or change log can help, but those records may not show the complete configuration. Screenshots become stale. And repeating a series of manual steps in another tenant leaves room for small differences to accumulate.
What changes with infrastructure as code?
With IaC, you describe the desired configuration in files. A tool such as Terraform uses a provider to communicate with a service’s API. The Jamf Pro Platform provider lets Terraform manage supported Jamf resources through that model.
Instead of making a change directly and documenting it afterward, the workflow becomes:
1
2
3
4
5
6
7
Describe the change in code
          |
          v
Review the proposed change
          |
          v
Approve and apply it to Jamf Pro
The code becomes a reviewable description of the objects you have chosen to manage. Git records how that description changes over time. Terraform’s plan shows the actions it proposes based on the configuration, its state, and what it can read from the provider.
That creates a useful pause before a change is applied. A reviewer can inspect whether Terraform plans to create, update, replace, or delete resources and decide whether the result matches the intent.
Why this matters to Jamf admins
Changes become easier to review
A pull or merge request can show the exact configuration change and give teammates a place to ask questions before it is applied. Instead of relying only on a summary such as “updated the Chrome policy,” a reviewer can see which settings or scope references changed and inspect the Terraform plan.
A plan is not a substitute for understanding Jamf impact. It is another piece of evidence for the review, and it can help surface changes that deserve closer attention.
Repeating configuration gets less error-prone
If you maintain development and production tenants, code gives you a consistent way to describe the objects that should be managed in both. Environment-specific values can still differ, but the shared configuration and the intentional differences are visible.
This does not make two Jamf tenants identical automatically. They may have different integrations, inventory, device populations, or operational requirements. The benefit is that you can distinguish deliberate differences from accidental ones.
History becomes useful to both admins and teammates
Version control keeps a history of changes to the configuration files: what changed, when it changed, and the discussion around it. That is valuable when troubleshooting a regression or onboarding someone new to the team.
Git history is not a complete audit trail of every action in Jamf Pro, and it does not replace Jamf logs or your organization’s change-management process. It gives you a clearer history of the configuration managed through the repository.
You can spot configuration drift
Drift happens when the live Jamf configuration no longer matches the configuration your team intends to manage as code. It can happen after a console edit, an emergency change, or a change made by another automation tool.
A Terraform plan can help identify differences for resources Terraform manages. That makes it easier to decide whether to update the code, keep the console change, or take another corrective action. Drift detection only applies to the resources and attributes supported by the provider and represented in your configuration; it is not a scan of every setting in Jamf Pro.
IaC is not an all-or-nothing project
You do not need to convert your entire Jamf environment before getting value from IaC. In fact, a smaller start is often easier to understand and safer to review.
Begin with an object that is useful but low-risk for your environment. For example, you might manage a category, a narrowly scoped policy, or a configuration that you can test with a small group of devices. The right first object depends on your tenant, provider support, and change-control requirements.
Before expanding, make sure your team understands where Terraform state is stored and who can access it. State helps Terraform associate resources in its configuration with objects it manages. It can contain sensitive data, so it needs appropriate access controls and storage. Committing configuration to Git does not by itself create a backup of your Jamf tenant, and Terraform state should not be treated as one.
You should also decide how the team will handle changes made directly in Jamf Pro. Some console work will remain necessary, especially for investigation and operational tasks. For objects managed by Terraform, however, an untracked console change can create drift or be changed again by a later Terraform run. Make the ownership boundary clear: which objects are managed as code, who may change them, and how emergency changes are reconciled back into the repository.
A realistic destination
A mature workflow might use GitLab to run Terraform validation and generate a plan for review. After approval, the plan can be applied to a development tenant first. Production changes can follow a separate promotion and approval process.
For example:
1
2
3
4
5
6
7
8
9
10
Feature branch
      |
      v
Review configuration and plan
      |
      v
Apply to development
      |
      v
Promote reviewed change to production
You do not need this entire pipeline on your first day. Start by understanding the configuration and plan locally in a non-production environment. Add shared state, automated checks, and controlled applies as your process and team are ready for them.
The payoff
Infrastructure as code gives Jamf admins a way to make selected configuration more transparent and repeatable. It can make reviews more concrete, clarify differences between environments, and help teams investigate drift.
It also asks for new habits. Terraform state must be protected. Plans need to be read rather than blindly approved. Provider coverage has limits, and console changes need a clear ownership process. IaC makes change management more explicit; it does not remove the need for good judgment.
The best starting point is not “move everything to Terraform.” It is to pick one appropriate object, understand what Terraform proposes to do with it, and build confidence in the workflow before expanding.
In the next post, we’ll translate Terraform’s core concepts—resources, variables, outputs, providers, state, plans, and applies—into terms that make sense to a Jamf administrator.